Manage Secrets in GCP Secret Manager
GCP Secret Manager is a fully managed service for storing, managing, and accessing sensitive information such as API keys, passwords, and certificates. It allows you to store secrets centrally with encryption, automate versioning, and control access using Google Cloud’s IAM policies.
This guide will show you how to use GCP Secret Manager to manage user credentials for authentication plugin key-auth and how to retrieve the secret in APISIX.
Prerequisite(s)
- Install Docker.
- Install cURL to send requests to the services for validation.
- Follow the Getting Started tutorial to start a new APISIX instance in Docker.
- Have a GCP account and enable Secret Manager.
Create a Secret in GCP Secret Manager
In this section, you will be creating a secret to store the key-auth authentication key for consumer john.
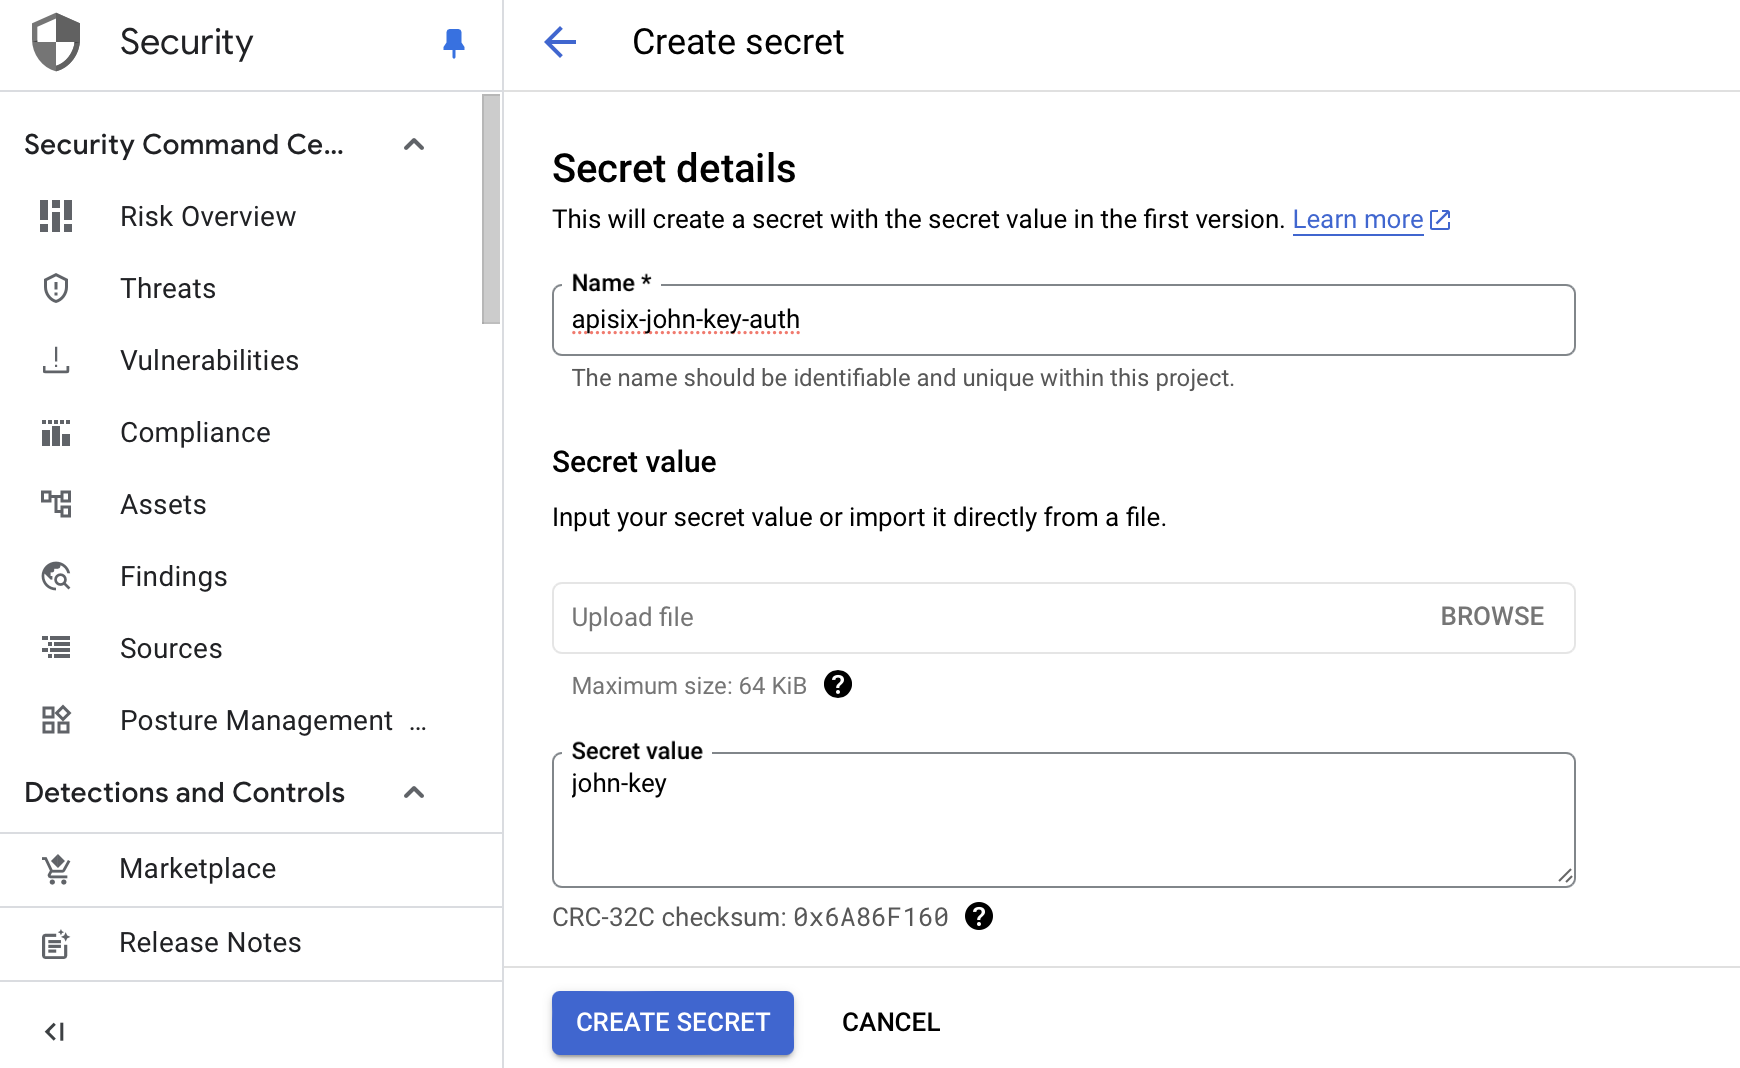
Navigate to GCP Secret Manager in the console and create a secret. Fill in the name apisix-john-key-auth and the secret john-key:
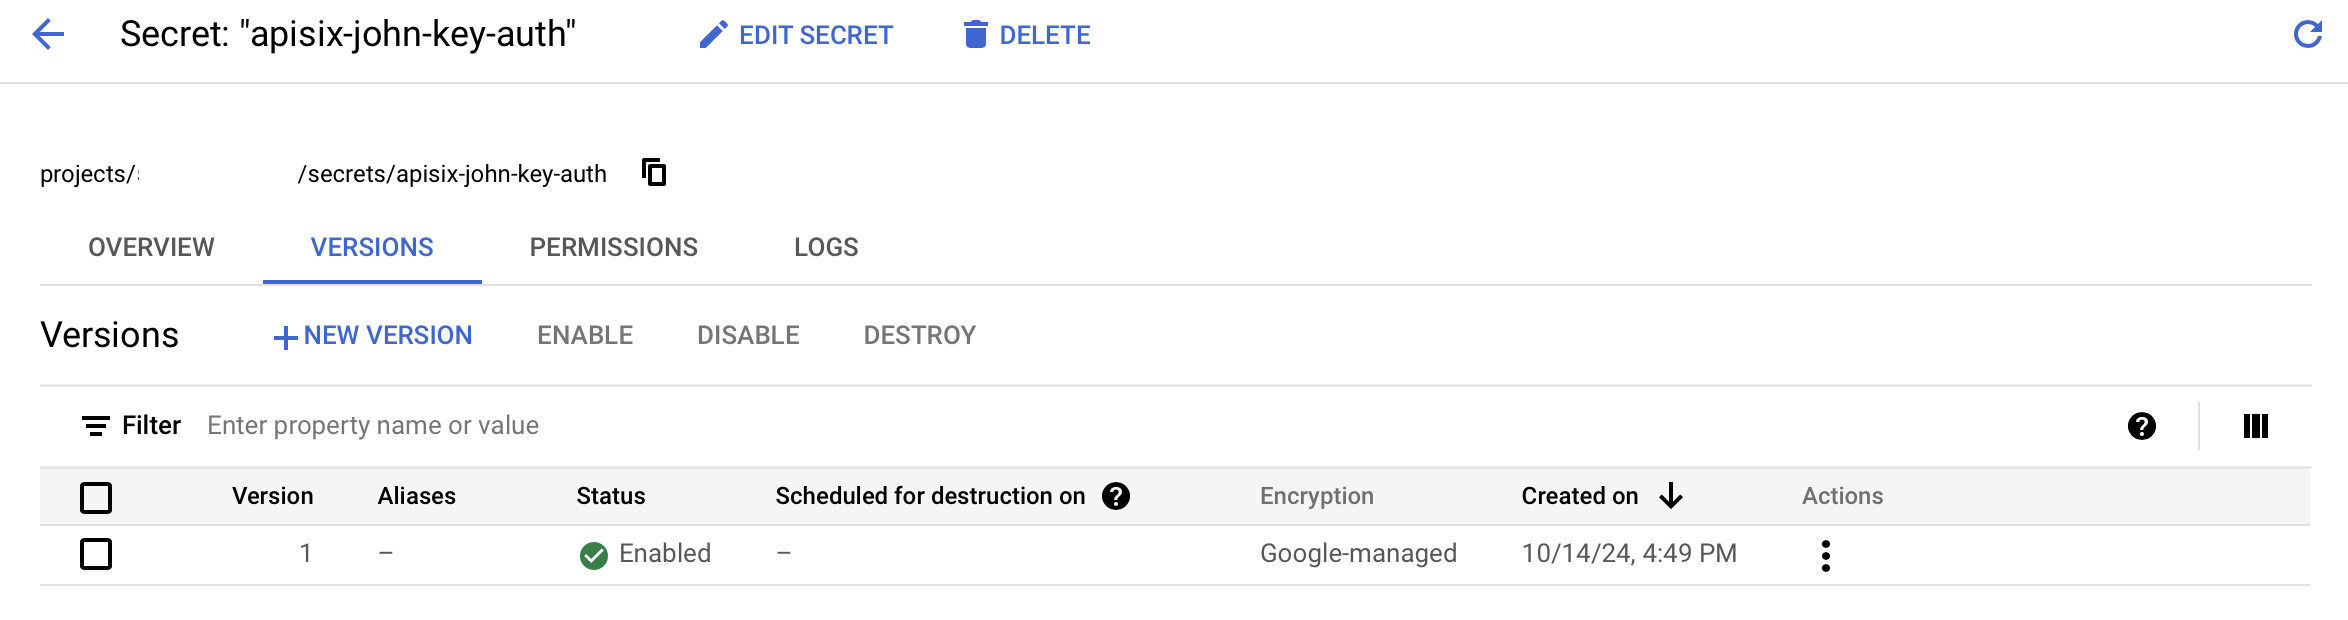
Review the rest of the information and finish secret creation. You should see the secret listed in GCP Secret Manager:
Obtain GCP Access Credentials
Follow the service account credentials doc to create a service account in GCP, assign the account with the Secret Manager Secret Accessor role, and create credentials for the account.
You should see a JSON file containing the credentials generated and downloaded to your machine, similar to the following:
{
  "type": "service_account",
  "project_id": "apisix-project",
  "private_key_id": "f039bb20b2xxxxxxxxxb43cb7132axxxxxx1f165",
  "private_key": "-----BEGIN PRIVATE KEY-----\n...\n-----END PRIVATE KEY-----\n",
  "client_email": "apisix-secret-manager@apisix-project.iam.gserviceaccount.com",
  "client_id": "115458xxxxxxx68702206",
  "auth_uri": "https://accounts.google.com/o/oauth2/auth",
  "token_uri": "https://oauth2.googleapis.com/token",
  "auth_provider_x509_cert_url": "https://www.googleapis.com/oauth2/v1/certs",
  "client_x509_cert_url": "https://www.googleapis.com/robot/v1/metadata/x509/apisix-secret-manager%40apisix-project.iam.gserviceaccount.com",
  "universe_domain": "googleapis.com"
}
Update Trusted Certificates in APISIX
Steps in this section are only required if you use the default configuration with SSL verification. If you wish to disable SSL verification, set ssl_verify to false in the next step.
Update the path to the CA certificates in the configuration file:
docker exec apisix-quickstart /bin/bash -c "echo '
apisix:
  ssl:
    ssl_trusted_certificate: /etc/ssl/certs/ca-certificates.crt
  enable_control: true
  control:
    ip: "0.0.0.0"
    port: 9092
deployment:
  role: traditional
  role_traditional:
    config_provider: etcd
  admin:
    admin_key_required: false
    allow_admin:
      - 0.0.0.0/0
plugin_attr:
  prometheus:
    export_addr:
      ip: 0.0.0.0
      port: 9091
  ' > /usr/local/apisix/conf/config.yaml"
Reload APISIX for configuration changes to take effect:
docker exec apisix-quickstart apisix reload
Configure Secret in APISIX
Configure GCP Secret Manager to be a secret provider for john with the access credentials obtained in the last step:
curl "http://127.0.0.1:9180/apisix/admin/secrets/gcp/john" -X PUT -d '
{
  "auth_config": {
    "client_email": "apisix-secret-manager@apisix-project.iam.gserviceaccount.com",
    "private_key": "-----BEGIN PRIVATE KEY-----\n...\n-----END PRIVATE KEY-----\n",
    "project_id": "apisix-project"
  },
  "ssl_verify": true
}'
❶ Replace with your client email.
❷ Replace with your private key.
❸ Replace with your project ID.
❹ Enable SSL verification (default).
Create a Consumer and its Credential
Create a consumer john:
curl "http://127.0.0.1:9180/apisix/admin/consumers" -X PUT -d '
{
  "username": "john"
}'
Configure the key-auth credential for consumer john to fetch the key from secret provider:
curl "http://127.0.0.1:9180/apisix/admin/consumers/john/credentials" -X PUT -d '
{
  "id": "cred-john-key-auth",
  "plugins": {
    "key-auth": {
      "key": "$secret://gcp/john/apisix-john-key-auth"
    }
  }
}'
Create a Route with Authentication
Create a sample route and enable the key-auth plugin:
curl "http://127.0.0.1:9180/apisix/admin/routes" -X PUT -d '
{
  "id": "key-auth-route",
  "uri": "/anything",
  "plugins": {
    "key-auth": {}
  },
  "upstream" : {
    "nodes": {
    "httpbin.org": 1
    }
  }
}'
Verify
Send a request to the route with the valid credential:
curl -i "http://127.0.0.1:9080/anything" -H 'apikey: john-key'
You should receive an HTTP/1.1 200 OK response.
Send a request to the route with an invalid credential:
curl -i "http://127.0.0.1:9080/anything" -H 'apikey: wrong-key'
You should receive an HTTP/1.1 401 Unauthorized response.
Next Steps
You have now learned how to configure APISIX to fetch secrets from GCP Secret Manager.
In addition to GCP Secret Manager, APISIX also supports the integration with HashiCorp Vault and AWS Secrets Manager for secret management.